Data perimeter
This is one policy kind in the ADR-014 governance engine. Policies resolve most-specific-wins with deny-wins at a tie, across scopes that run agent → user/role → workspace → team → org. Rules of the same kind combine rather than replace, so what matters is which rules exist, not which policy row holds them.
What it does
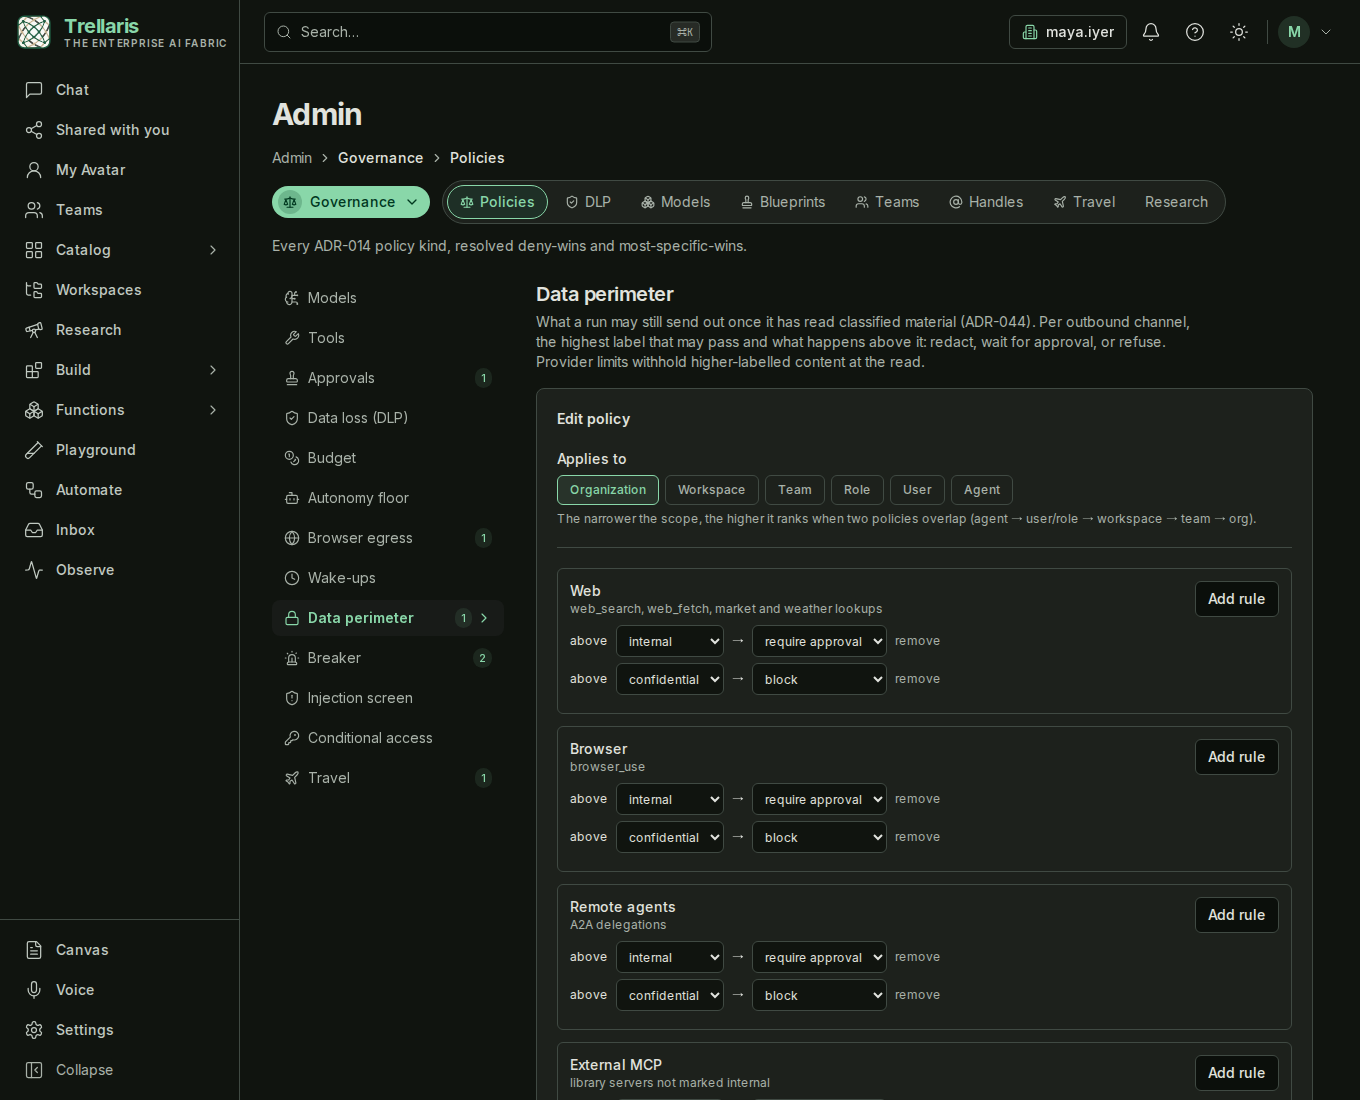
A data perimeter policy says, per outbound channel, the highest classification a run may carry and still use that channel freely, and what happens above it. It is evaluated against the run's taint, the highest label the run has read, immediately before each outbound tool call, in the same place the approval gate runs.
Channels
| Channel | Covers |
|---|---|
web | web_search, web_fetch and other tools that send text to the public internet. |
browser | browser_use: typing into a page, submitting a form. |
a2a | Delegating to a remote agent. A run that is a remote call counts as this channel from the start. |
mcp_external | Tools on an MCP server the organisation marked external. |
connector_write | Write operations on connectors (tickets, records, files). |
email | Sending or drafting mail through a connector. |
Actions
| Action | Effect above the channel's limit |
|---|---|
redact | The outgoing text is passed through DLP redaction before it leaves. The call proceeds. |
require_approval | The run parks for approval exactly as a connector write does, with the channel and the taint in the approval card. The approver is whoever the organisation's approval policy names. On a remote-agent run this acts as block: there is no call to park. |
block | The call is refused with a typed error the agent relays to the person. A refusal on Restricted material opens an incident. |
Provider limits
The other half of the policy caps the label a model provider may receive. A chunk above the cap is withheld at the read, the agent is told some material could not be used, and the run continues. Nothing is sent and then filtered; the content never moves.
The default
Every organisation starts with one org-scoped row: on web,
browser, a2a and mcp_external,
Confidential material waits for approval and Restricted material is refused.
Internal and Public material is unaffected on every channel, and no provider
limit is set. Because everything that existed before labels carries Internal,
nothing that worked before changes until someone labels something.
Floors
Under ADR-030 a floored perimeter is a minimum a narrower scope may only tighten. Channel rules union across scopes, so a team can add a rule but never remove one; a provider limit takes the lower label of the two.